UK GDPR · EU GDPR · Data Protection for Non-UK Companies
UK GDPR Representative for Companies Outside the UK
If your business is based in the UAE, the Gulf or elsewhere outside the UK, but sells to or monitors people in the UK, the UK GDPR may require you to appoint a representative in the UK. We assess whether the rule applies to you, prepare the documentation, and set up your UK representation as your point of contact with the ICO and with individuals.
The Legal Requirement
Article 27: A Rule Many Non-UK Companies Miss
Under Article 27 of the UK GDPR, a controller or processor that is not established in the UK, but offers goods or services to individuals in the UK or monitors their behaviour, must designate in writing a representative established in the UK. The EU GDPR contains a parallel rule for companies outside the EU that target individuals in EU member states.
The representative is the point of contact for the Information Commissioner’s Office (ICO) and for data subjects, and keeps a copy of your records of processing. Failing to appoint one where required is a breach in itself and can attract enforcement action and fines — and it is often the first thing a regulator checks when a complaint arrives.
- 01
E-Commerce & SaaS
Online shops, apps and software services that sell to customers in the UK.
- 02
Tracking & Analytics
Websites and platforms that profile or monitor the behaviour of UK users.
- 03
AI & Data Services
AI tools and data-driven services processing personal data of people in the UK.
- 04
Limited Exemptions
Only occasional, low-risk processing that does not involve large-scale sensitive data is exempt.
Our Services
Representation and Data Protection Compliance
A practical package for growing companies that need to meet UK data protection rules without opening a UK office.
Applicability Assessment
A written analysis of whether Article 27 of the UK GDPR, and the equivalent EU GDPR rule, applies to your activities and which exemptions may be available.
UK Representative Service
Written mandate, a UK address for your privacy notice, and handling of correspondence from the ICO and individuals, with prompt forwarding to your team. Contact us for current availability.
Records of Processing
Preparation and maintenance of your Article 30 records of processing activities, which the representative must be able to provide on request.
Privacy Notices & Policies
Privacy notices, cookie notices and internal data protection policies drafted for UK and EU requirements.
Data Subject Requests
Support in answering access, erasure and objection requests within the statutory time limits.
International Data Transfers
Transfer mechanisms for sending personal data between the UK, the EU, the UAE and other countries, including transfer risk assessments.
AI & Data Protection
Data protection impact assessments and lawful-basis analysis for AI systems, alongside EU AI Act readiness.
Breach Response
Guidance on assessing personal data breaches and notifying the ICO and affected individuals where required.
Staff Training
Short data protection training for teams handling UK and EU customer data.
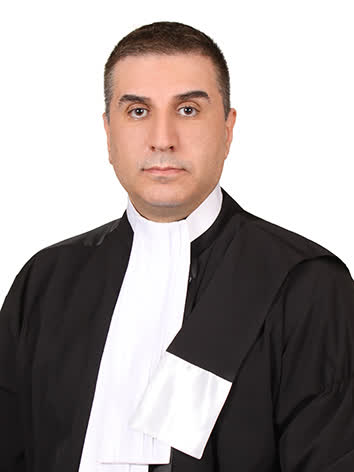
Your Adviser
Dr. Ahmadreza Moini
Dr. Moini is a member of the Iran Bar Association and the Tehran Arbitrators Association, a university lecturer and specialist in information law, privacy and AI regulation. He teaches information law, privacy and electronic commerce law at university level, and his doctoral research examined the legal status of data messages and digital assets across Iranian, English and US law.
Through PAD International Group, with an office in the Sharjah Publishing City Free Zone, he advises companies in the UAE and the wider region that do business with customers in the UK and Europe — combining data protection compliance with AI and e-commerce law.
How It Works
Compliant in Four Steps
Free Initial Check
A short call to understand what you sell, to whom, and what personal data you process.
Assessment
A written view on whether a UK or EU representative is required and what else needs fixing.
Appointment
Signed mandate, updated privacy notice and records of processing in place.
Ongoing Service
Annual service covering regulator and data subject contact, with updates as the law changes.
Common Questions
UK GDPR Representative — FAQ
Get Started
Find Out If You Need a UK Representative
Tell us where your company is based, what you sell and where your customers are. We will tell you whether Article 27 applies and what it takes to comply.
Request a Free Initial CheckThe Role in Practice
What a UK Representative Does for You
Contact Point for the ICO
Receives enquiries from the Information Commissioner’s Office on your behalf and passes them to your team quickly, so that deadlines are not missed.
Contact Point for Individuals
Gives UK customers a local address to exercise their rights, such as access, correction and erasure requests, and forwards each request to you.
Keeps Your Records
Holds a copy of your records of processing activities under Article 30 and makes them available to the ICO on request.
Cooperation with the Regulator
Supports cooperation with the ICO under Article 31, including responding to information requests and coordinating with your management.
Visible in Your Privacy Notice
Is named, with contact details, in your privacy notice, showing customers and partners that you take UK data protection seriously.
Logging & Reporting
Keeps a log of all correspondence received and reports regularly to you, so you have a clear record if a dispute or investigation arises.
Quick Self-Check
Signs Your Company May Need a UK Representative
If your company has no office in the UK, read through the points below. If any of them describe your business, a short assessment is worthwhile.
- ✓Prices in GBPYour website or app shows prices in pounds sterling.
- ✓Delivery to the UKThe UK appears in your shipping options or delivery table.
- ✓UK-targeted marketingYou run ads, influencer campaigns or email marketing aimed at people in the UK.
- ✓Tracking & analyticsYou use cookies, pixels or analytics that monitor the behaviour of UK visitors.
- ✓UK customers on fileYour CRM, newsletter list or order history contains people in the UK.
- ✓Apps & SaaSYour app is available in the UK app stores, or UK users sign up to your platform.
- ✓UK presence signalsYou use a .co.uk domain, a UK phone number or UK-specific content.
- ✓Also selling into the EUYou target customers in EU countries too, which may require an EU representative as well.
At a Glance
UK Representative vs EU Representative
Since Brexit, the UK GDPR and the EU GDPR apply separately. A company outside both that targets customers in the UK and in the EU may need two representatives.
| UK Representative | EU Representative | |
|---|---|---|
| Legal basis | Article 27 UK GDPR | Article 27 EU GDPR |
| Where established | In the United Kingdom | In an EU member state where your customers are |
| Regulator | Information Commissioner’s Office (ICO) | Data protection authorities of the EU member states |
| Appointment | Written mandate | Written mandate |
| Privacy notice | Must name the UK representative | Must name the EU representative |
| Main exemption | Occasional processing that is unlikely to result in a risk to individuals and does not include large-scale sensitive or criminal-offence data; public authorities | |
| Maximum fine for failing to appoint | £8.7 million or 2% of worldwide annual turnover | €10 million or 2% of worldwide annual turnover |
Get Started
Find Out If You Need a UK Representative
Tell us where your company is based, what you sell and where your customers are. We will tell you whether Article 27 applies and what it takes to comply.
Request a Free Initial CheckOr contact us directly: +44 7368 955207 · a.moini@padinternationalgroup.com